Service 03 of 05
Security Incident Monitoring
Real-time observation of anomalies, unauthorized access attempts, and abnormal system behaviors.
Accelerates threat detection timelines and minimizes potential operational impact.
Overview
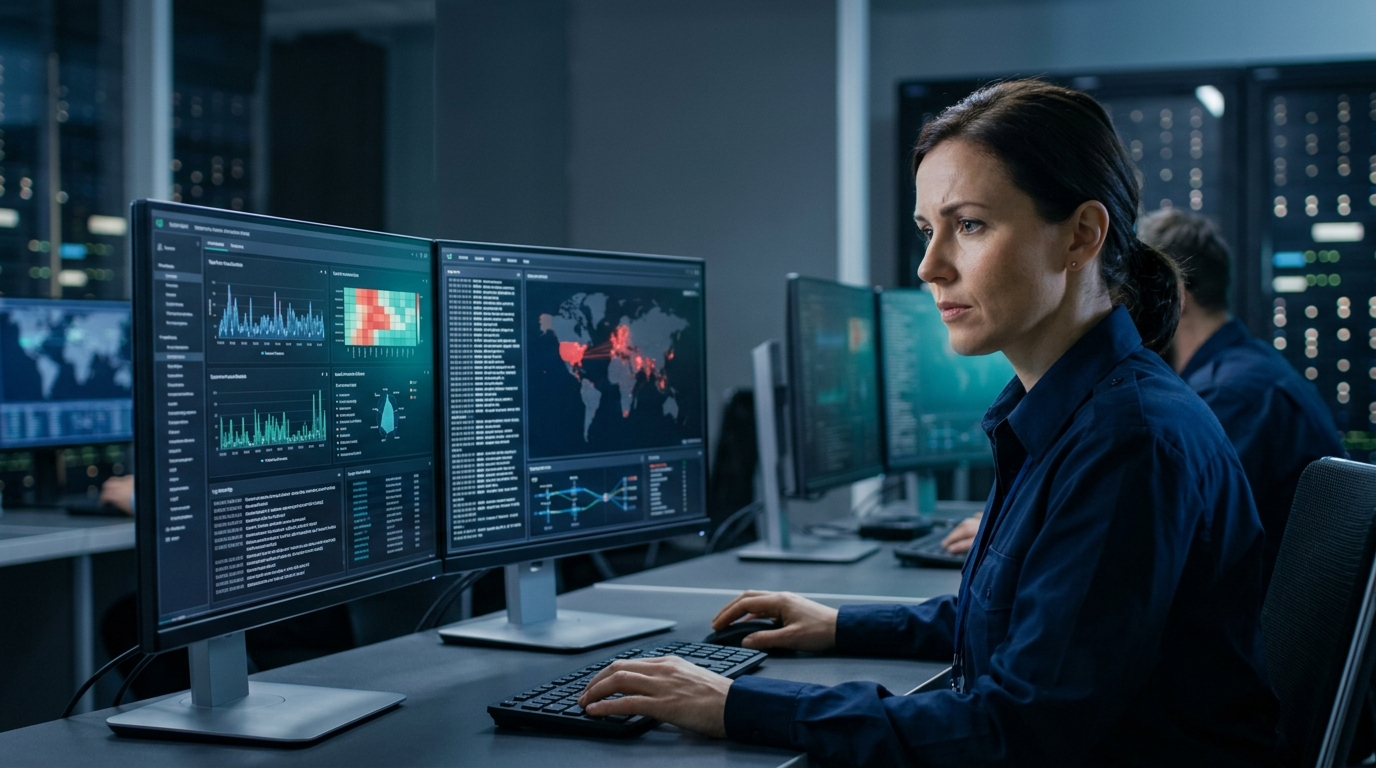
Audit logs explain what happened; monitoring helps teams notice it while it is still happening. The earlier an unusual login pattern, an unexpected privilege change, or an abnormal process is seen, the smaller its potential impact on operations.
PhotonPeak develops security incident monitoring that observes activity as it is recorded. It highlights anomalies, unauthorized access attempts, and abnormal system behaviors, and links each alert back to the underlying audit records so responders can see the full context.
What it covers
- Anomaly observation
- Comparison of current activity against expected patterns for users, hosts, and services to surface unusual behavior.
- Access attempt tracking
- Visibility into failed authentication bursts, access from unexpected locations, and attempts to reach restricted resources.
- Behavior changes on systems
- Detection of abnormal process activity, configuration changes, and unexpected privilege escalation.
- Alert context
- Each alert carries the related events, affected assets, and identities involved, reducing time spent gathering information.
- Routing and triage
- Rules for prioritizing and directing alerts to the responsible team or channel.
- Link to the audit trail
- Direct navigation from an alert to the complete, retained log history for follow-up investigation.
Applicable scenarios
Security Incident Monitoring is typically relevant in situations such as:
- Security operationsSupporting teams that watch enterprise activity and respond to potential threats.
- Identity misuseSpotting credential misuse or account takeover attempts early.
- Insider riskNoticing unusual data access or administrative activity by internal accounts.
- Infrastructure changesFlagging unexpected configuration changes in cloud and on-premises systems.
How we work together
Collaboration starts with an email to info@photonpeak.online. From there, a typical path looks like this:
- Initial emailShare a short description of your environment and what you need from incident monitoring.
- Requirements discussionWe go through your current setup and constraints in more detail.
- Capability reviewWe review how the software capabilities above apply to your systems.
- Deployment planningWe agree on secure deployment steps and the order in which to approach them.
To make the first conversation productive, it helps to mention the systems you most need to watch, how alerts are handled today, who responds to them, and any recurring incident types you want to detect earlier.
Discuss incident monitoring with PhotonPeak Inc
Send us an email describing your environment and requirements. We will reply to continue the conversation.