Service 01 of 05
Enterprise Audit Log Management Software
Centralized ingestion, indexing, and structuring of operational logs across complex distributed enterprise environments.
Enables rapid forensic investigations and eliminates blind spots in high-volume system activity.
Overview
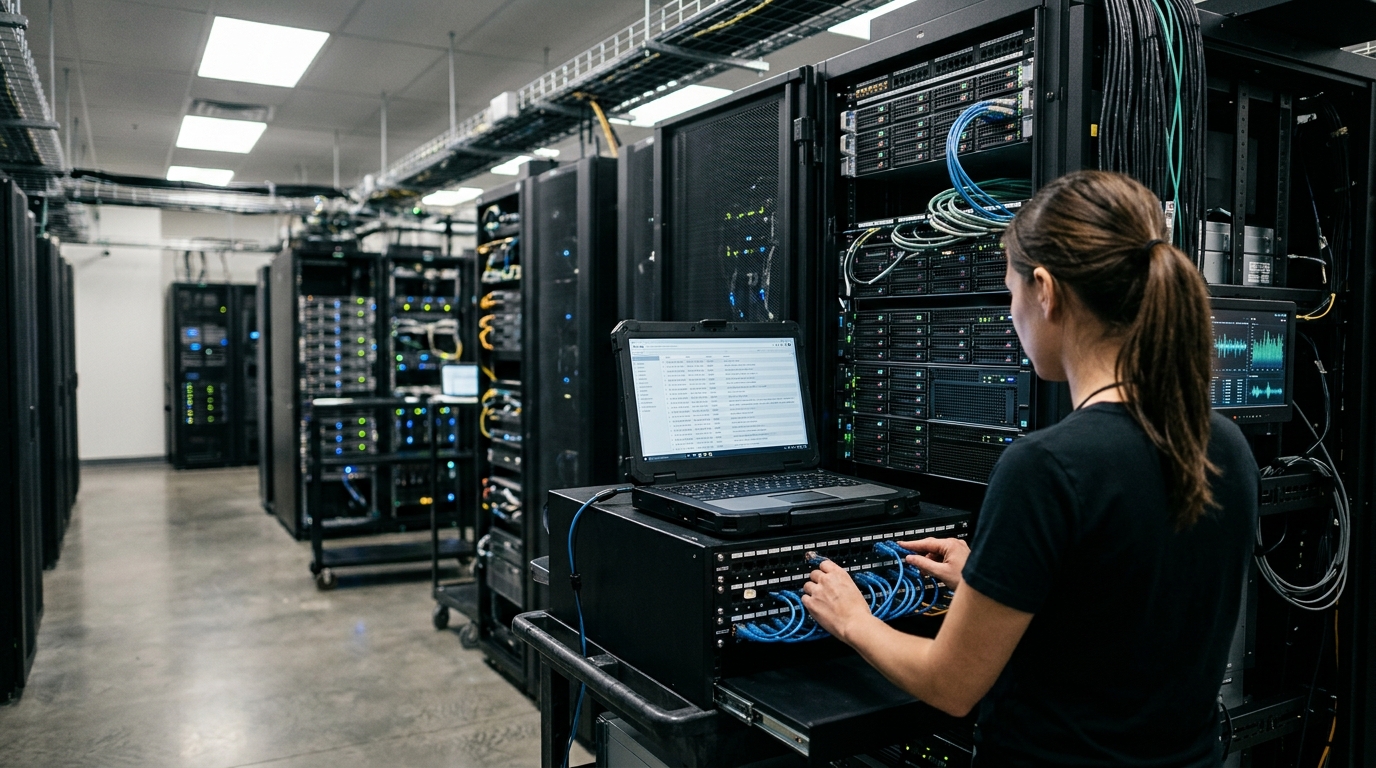
Every server, application, identity provider, and network device writes its own account of what happened. On their own these records are scattered across formats, time zones, and storage locations, which makes them hard to trust and slow to search when an answer is needed.
PhotonPeak develops audit log management software that brings those records together. Logs are collected from distributed sources, normalized into a consistent structure, and indexed so that security, operations, and audit teams can ask precise questions of a single, coherent history.
What it covers
- Distributed ingestion
- Collection of operational and audit events from servers, applications, databases, network equipment, and cloud services across multiple sites and environments.
- Normalization and structure
- Parsing of varied log formats into consistent fields such as actor, action, target, source, and timestamp, so records from different systems can be compared directly.
- Indexing and search
- Indexes designed for high event volumes, allowing investigators to filter by user, host, time window, or event type without manual file collection.
- Cross-system correlation
- Linking related events from different systems into a single timeline to reconstruct the sequence of an incident or change.
- Retention policies
- Configurable rules for how long each category of record is kept, aligned with internal policy and regulatory obligations.
- Controlled access
- Role-based access to log data, so sensitive records are visible only to the people responsible for reviewing them.
Applicable scenarios
Enterprise Audit Log Management Software is typically relevant in situations such as:
- Forensic investigationReconstructing who did what, when, and from where after a suspected incident.
- Privileged activity reviewTracing actions taken by administrators and service accounts across systems.
- Consolidation after changeBringing logs together after a migration, reorganization, or the addition of new platforms.
- Answering audit requestsProducing complete event histories for a specific system, user, or period on request.
How we work together
Collaboration starts with an email to info@photonpeak.online. From there, a typical path looks like this:
- Initial emailShare a short description of your environment and what you need from audit log management.
- Requirements discussionWe go through your current setup and constraints in more detail.
- Capability reviewWe review how the software capabilities above apply to your systems.
- Deployment planningWe agree on secure deployment steps and the order in which to approach them.
To make the first conversation productive, it helps to mention the approximate number and types of log sources, typical daily volume, required retention periods, and the tools currently used to collect or search logs.
Discuss audit log management with PhotonPeak Inc
Send us an email describing your environment and requirements. We will reply to continue the conversation.